We perform QA security testing for all kinds of software to guarantee
its reliable protection against intruders.

Our Security Testing Services

Web App Security Testing
Our security testing company protects web applications against the OWASP Top 10 — injection, XSS, CSRF, broken access control, and session flaws. Manual and automated checks keep your web app resilient without slowing releases

Mobile App Security Testing
QAwerk’s security testing services validate iOS and Android apps for secure storage, transport-layer protection, permissions, and platform-specific risks. Your mobile app stays safe on every device your users rely on.

API Security Testing
Our security testing services cover REST and GraphQL endpoints: authentication, broken object-level authorization, rate limits, and data exposure. Reliable APIs mean partners and mobile clients connect without opening new attack surfaces.
Website Security Testing
As part of our security testing services, website checks harden public-facing sites against injection, XSS, CSRF, misconfigurations, and risky third-party scripts. Your visitors get a site that protects their data at every interaction.
Access Control & Authentication Testing
QAwerk’s security testing company verifies roles, permissions, MFA, session handling, and password-reset flows. Only the right users reach the right data, and privilege escalation paths are closed before release.
Vulnerability Scanning & Configuration Review
Our security testing services combine automated scans with expert-led review of HTTP headers, TLS, CORS, error handling, and cloud configuration. Known CVEs, misconfigurations, and outdated components are caught early in the QA cycle.
Selected Cases
These projects show how QAwerk validates security-sensitive products across fintech, identity verification, and healthcare, where authentication, data exposure, and access-control issues carry the highest cost.

Union54

Thirdfort
ChitChat
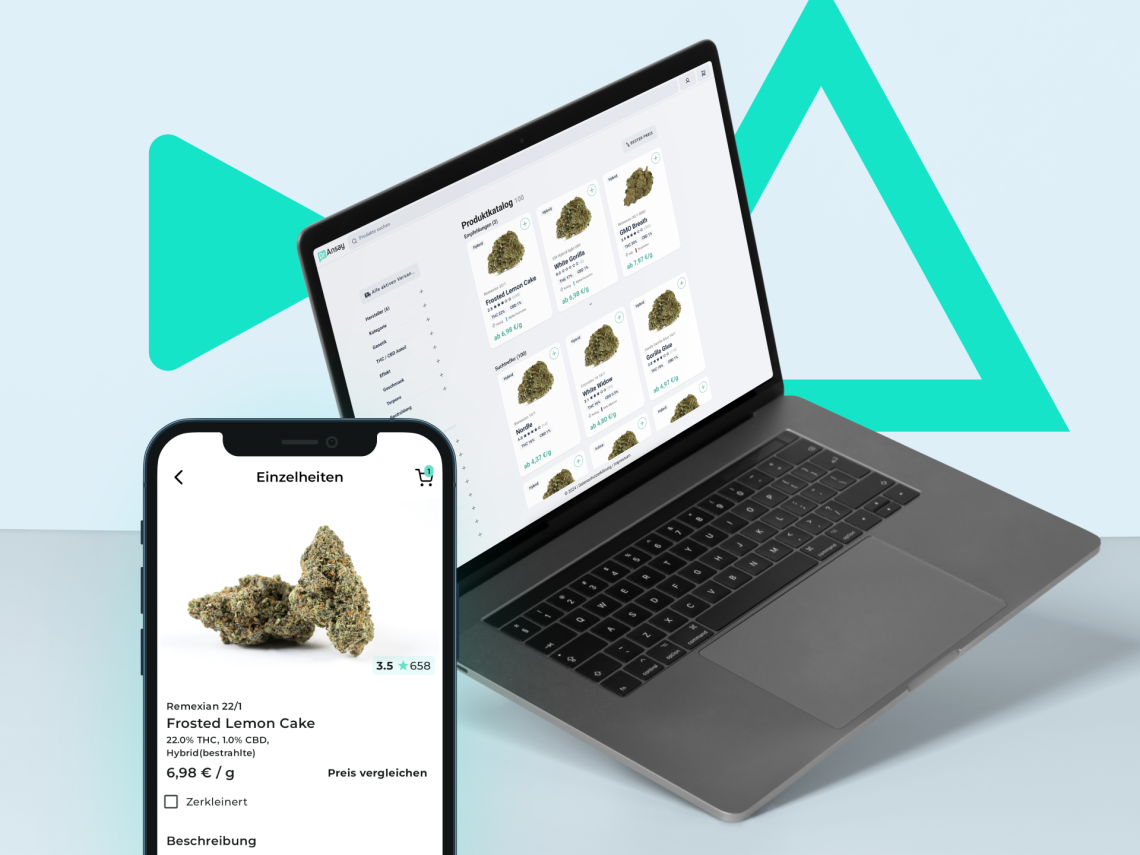
DrAnsay
Need a security testing company?
Contact UsWhy Choose QAwerk as Your Security Testing Company
OWASP-Aligned Methodology
Our security testing services follow OWASP guidelines end-to-end, covering the OWASP Top 10, ASVS, and MASVS checklists so findings map to the standards your auditors and clients already recognize.
Manual Expertise + Automated Coverage
Skilled engineers combine hands-on testing with automated tooling (OWASP ZAP, Burp Suite, Postman) to catch both the classic vulnerabilities scanners find and the logic flaws only a human notices.
Compliance-Ready Reporting
Findings come with severity, reproduction steps, and remediation guidance developers can act on immediately, mapped to GDPR, HIPAA, PCI-DSS, SOC 2, or ISO 27001 controls when your project requires it.
Security Built Into Everyday QA
Instead of one-off audits, our security testing company integrates checks into your regular QA cycles. Vulnerabilities surface early: before release, alongside functional, performance, and UX bugs.
Coverage Across Web, Mobile, and API
One team tests the full product surface: web apps, iOS and Android, and the APIs behind them, so nothing falls through the cracks between platforms.
Confidentiality by Default
Every engagement starts with an NDA and strict access controls. Test data, credentials, and findings stay within a small, named team — no shared drives, no leaked reports.

The QA team has been a great help for the release of our new offering, Unfold for Brands. The team has really put themselves in the place of the user to find any bugs or user experience issues, mitigating any potential issues at launch.


We've worked with QAwerk to handle the QA of our native desktop app. They've done a tremendous job and even went out of their way to ensure the quality of the app. We'll continue working with them in the future.

Other Services We Provide
Penetration Testing Services
Our specialists simulate real-world attacks to expose exploitable weaknesses, chain vulnerabilities together, and prove business impact, going beyond what routine security testing surfaces.

Performance Testing
Our engineers stress your system under peak load and traffic spikes, catching stability and scalability issues that also expose your app to denial-of-service and resource-exhaustion risks.
Compliance Testing
We validate your product against GDPR, HIPAA, PCI-DSS, SOC 2, and ISO 27001 requirements, mapping every finding to the specific control your auditors expect to see evidence for.
Automated Testing
We build automated suites that plug into your CI/CD pipeline, so functional regressions and security regressions are caught on every commit rather than at the end of a release cycle.
API Testing
We verify functional correctness, contracts, and error handling for REST and GraphQL APIs, giving your integrations a solid foundation before layering security-specific checks on top.
Manual QA Testing
Skilled testers explore your product the way a real user or a real attacker would, uncovering logic flaws and edge-case behaviors that automated scanners consistently miss.
Security Testing Tools We Use
FAQ
What is security testing?
Security testing is a set of QA activities that verify a software product protects data and functionality against unauthorized access, misuse, and known vulnerabilities. It covers authentication, authorization, confidentiality, integrity, availability, and non-repudiation across web, mobile, and API.
What is the difference between security testing and penetration testing?
Security testing is a continuous, QA-integrated practice run alongside functional testing to catch vulnerabilities early in the release cycle. Penetration testing is a deeper, adversarial engagement that simulates real attacks to prove exploitability and business impact. QAwerk offers penetration testing as a separate, specialist-led service.
What are the main types of security testing?
The most common types are vulnerability scanning, security auditing, penetration testing, risk assessment, ethical hacking, posture assessment, and static and dynamic application security testing (SAST/DAST). Most engagements combine several of these.
How often should security testing be performed?
At minimum, before every major release and after any significant change to authentication, authorization, third-party integrations, or infrastructure. Products handling regulated or sensitive data typically run security testing continuously as part of the QA cycle, with a full assessment at least once a year.
Related in Blog
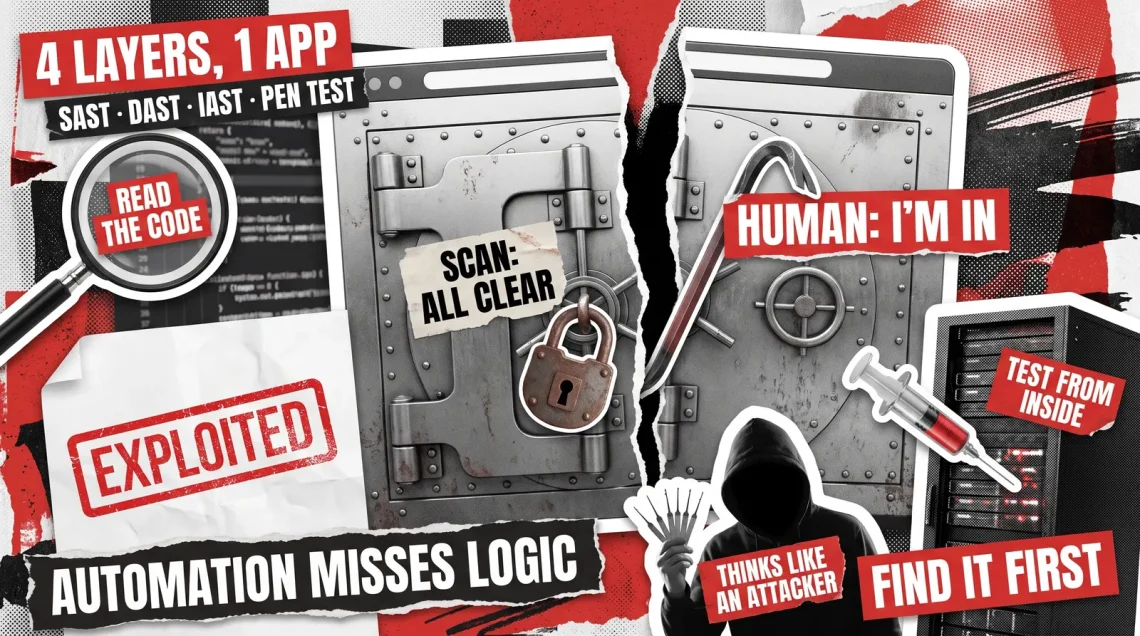
Web Application Security Testing: A Complete Guide
Web application security testing explained: what SAST, DAST, IAST, and pen testing each catch, and how to combine them across your release cycle....
Read More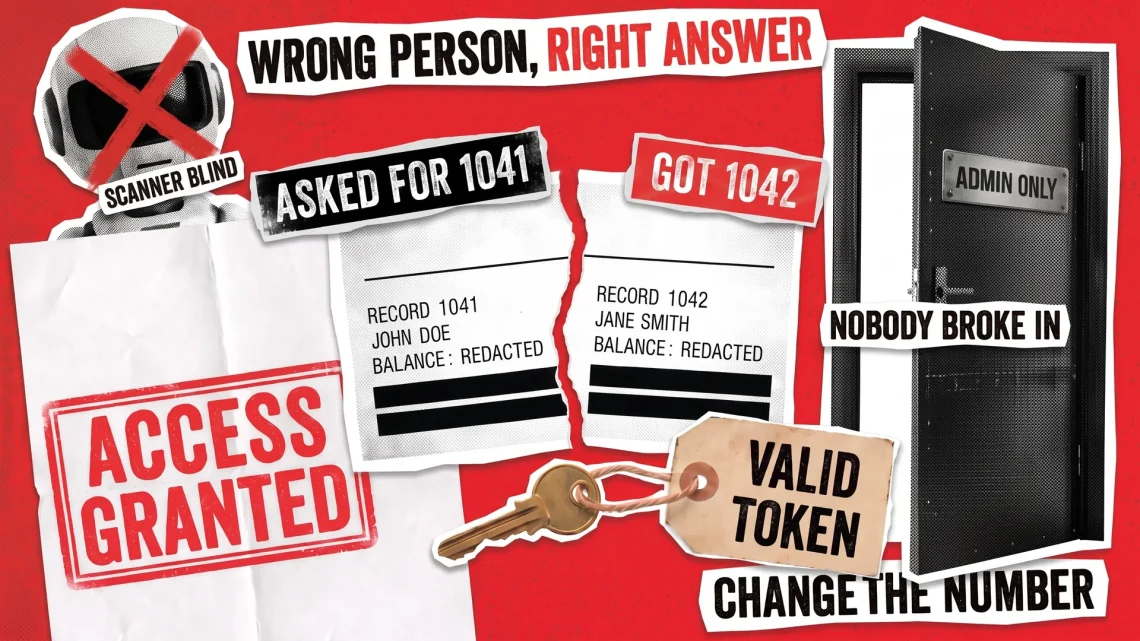
API Security Testing: A Complete Guide
What API security testing involves, the OWASP API Security Top 10, and how it differs from web app security testing. A practical guide, not a vendor pitch....
Read More
REST API Security Testing Checklist
A REST API security testing checklist covering auth, BOLA, rate limits, CORS, JWT and input validation. Run it every release with two ordinary accounts....
Read More
Google Play Data Safety Form: When It Doesn’t Match Your App
A Google Play data safety form that contradicts your app gets rejected or pulled. Here's how to check the declaration before Google does it for you....
Read MoreLooking for a trusted security testing team?
Get OWASP-aligned security testing services designed to protect your users and your business.
300+
TESTING PROJECTSACCOMPLISHED
12M+
TOTAL USERS OFAPPS WE’VE TESTED
65%
OF LONG-TERMCOLLABORATIONS
100%
DEADLINESMET