If your web app handles logins, payments, or customer data, someone will eventually ask you to prove it is secure: an enterprise buyer’s security questionnaire, an auditor, or your own board after a breach in your industry makes the news. A credible answer starts with knowing what web application security testing actually consists of, and which parts of it you are paying for when you run it in-house or bring in security testing services.
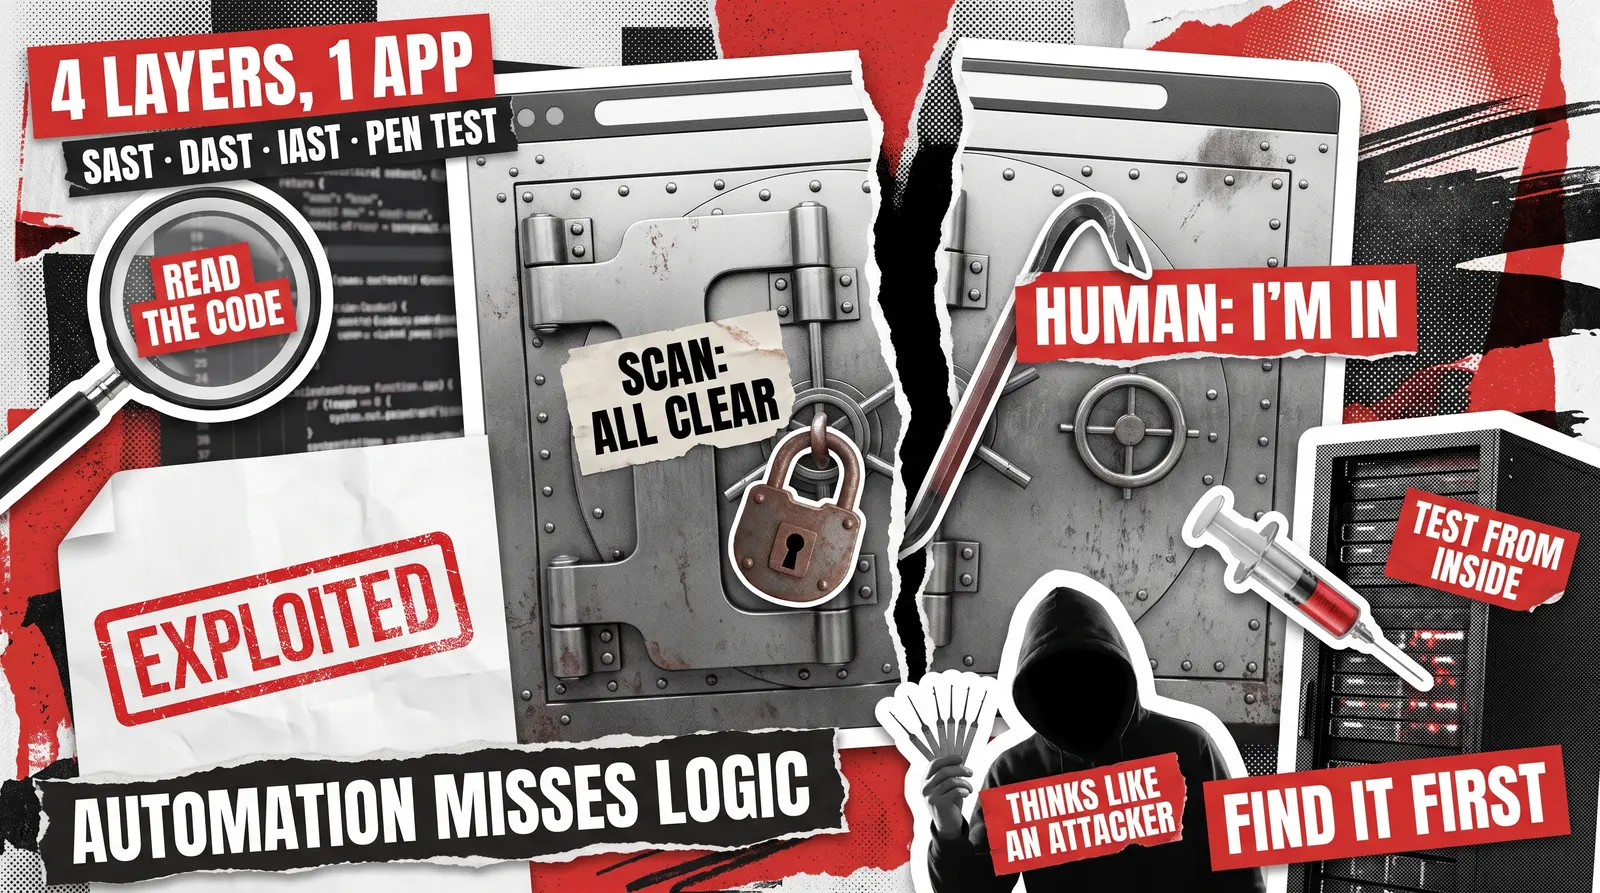
Web application security testing finds exploitable weaknesses in a web app before attackers do. It combines four approaches: static analysis of source code (SAST), dynamic testing of the running app from the outside (DAST), instrumented testing from inside the app at runtime (IAST), and manual penetration testing. Each catches a different class of flaw, so an effective program uses several of them.
The main cost decision is sequencing. Once set up, automated SAST and DAST scans cost little per run and can run on every build or every night. A manual penetration test of a mid-size web app usually takes one to three weeks of specialist time, which makes it the expensive layer and the one to schedule deliberately. Getting the order wrong usually means paying penetration testers to find issues a free scanner would have caught.
Below: what each approach does, where it falls short, and when you need which one.
The 4 Testing Approaches: SAST, DAST, IAST, and Pen Testing
The four approaches differ in what they look at and when they run. SAST reads the code before it ships, DAST and IAST test the application while it runs, and penetration testing puts a human attacker in front of it. Each one has blind spots the others cover, which is why mature programs run all four at different points in the release cycle.
Static Application Security Testing (SAST)
SAST scans source code, bytecode, or binaries without running the application. It traces how data flows from user input to sensitive operations and flags patterns such as unsanitized input reaching a database query, hard-coded secrets, and weak cryptography. It can run in a developer’s IDE or on every pull request, and it points to the exact file and line.
Its limit is context. SAST cannot see how the app is configured or deployed, and it often flags code paths that are unreachable in practice, so the first scan of an existing codebase tends to produce a long list that someone has to triage.
Software composition analysis (SCA) usually runs alongside SAST and checks third-party libraries for known vulnerabilities, the risk behind vulnerable and outdated components.
Dynamic Application Security Testing (DAST)
DAST tests the running application from the outside, the way an attacker would, with no access to the code. A scanner crawls the app, sends crafted requests to every input it finds, and reads the responses for signs of injection, cross-site scripting (XSS), missing security headers, exposed files, and misconfigured servers.
DAST finds issues that exist only once the app is deployed: server and TLS configuration, cookie flags, error pages that leak stack traces. It is weaker on anything a crawler cannot reach, such as pages behind multi-step authentication or single-page app routes that only appear after JavaScript runs. When it does find a problem, it reports a URL, and developers still have to locate the code.
Interactive Application Security Testing (IAST)
IAST places an agent inside the running application, in the language runtime or application server, and watches what the code does while the app is being exercised. When a test request carries input into a SQL query or a file path, the agent sees both the request and the exact line of code that handled it.
That combines the runtime view of DAST with the code-level precision of SAST, usually with fewer false positives than either. The catch is coverage: IAST only analyzes code paths that something actually executes, so its value depends on the quality of the functional and regression tests driving the app. It also needs an agent that supports your language and framework, and it adds some overhead to the test environment it runs in.
Manual Penetration Testing
A penetration test is a security specialist actively trying to break into the application with a real attacker’s goals: read another customer’s data, turn a regular account into an admin, or skip a payment step. Testers use scanners for coverage, then spend most of their time on what tools cannot judge, such as chaining two low-severity findings into a serious one, or abusing a workflow that is technically valid but was never meant to be allowed.
Of the four approaches, penetration testing is the one that reliably catches authorization flaws and business-logic abuse, and it produces evidence a buyer or auditor will accept. It is also a point-in-time snapshot and the most expensive layer per finding. Depending on how much the tester knows up front, a pen test runs as a black box, grey box, or white box engagement, which is how QAwerk structures its penetration testing services.
SAST vs DAST vs IAST vs Pen Testing at a Glance
What it examines
Source code, without running it
The running app, from outside
The running app, from inside via an agent
The running app, attacked by a human
When it runs
Every commit or pull request
Nightly or per release, against staging
During automated and functional test runs
Before major releases, after big changes, at least yearly
Catches well
Injection-prone code, hard-coded secrets, weak crypto
Misconfiguration, missing headers, reflected XSS, exposed files
Injection and data-flow flaws, with the exact line of code
Broken access control, business-logic abuse, chained exploits
Misses
Runtime and configuration issues
Code location, logic flaws, hard-to-crawl pages
Code paths no test executes
Anything outside the agreed scope and time box
False positives
High
Medium
Low
Very low, findings are verified by hand
Who acts on the results
Developers
DevOps and developers
Developers and QA
Engineering leads, security, compliance
How These Approaches Work Together
SAST catches issues earliest, while the fix is a one-line change in an unmerged branch, which makes it the cheapest layer to act on. SAST cannot tell you whether a flagged line is reachable, or whether the deployed server is configured safely.
DAST and IAST pick up what only shows at runtime. DAST checks the app as deployed, including the web server, TLS settings, and response headers. IAST confirms which data-flow issues are real by watching them happen, which is why it pairs well with an existing automated regression suite: the tests that already check features start checking security as well.
Manual penetration testing covers the class of flaw automation handles worst. A scanner can confirm that an endpoint requires a login. It cannot tell that a logged-in customer can change an order ID in the URL and see someone else’s invoice. Broken access control of this kind ranks first in the OWASP Top 10:2025, and finding it takes a person who understands what the app is supposed to allow. For what the manual layer looks like area by area, see our web application penetration testing checklist.
The OWASP Testing Methodology
The Open Worldwide Application Security Project (OWASP) publishes the Web Security Testing Guide (WSTG), the most widely referenced standard for how to test the security of a web application. Its current stable release, version 4.2, organizes active testing into 12 categories:
- Information gathering
- Configuration and deployment management testing
- Identity management testing
- Authentication testing
- Authorization testing
- Session management testing
- Input validation testing
- Testing for error handling
- Testing for weak cryptography
- Business logic testing
- Client-side testing
- API testing
Each category contains numbered test cases. Session management testing, for example, covers cookie attributes, session fixation, cross-site request forgery, logout behavior, and session timeout. Professional pen test reports often cite these IDs (WSTG-SESS-05 is the cross-site request forgery test) so every finding traces back to a documented procedure.
A workable mapping of WSTG categories to the four approaches:
- Information gathering, configuration, and client-side testing: largely automatable with DAST, with a person reviewing what the scanner flags.
- Input validation and weak cryptography: well covered by SAST in the code and by DAST or IAST at runtime.
- Authentication and session management: partly automatable, but lockout, password reset, and session timeout behavior need a tester stepping through the flows.
- Authorization and business logic: almost entirely manual penetration testing.
Its companion standard, the OWASP Application Security Verification Standard (ASVS), defines security requirements at three levels of rigor, which helps you decide how deep testing needs to go for your app.
Building a Web Application Security Testing Program
A testing program follows the software development lifecycle (SDLC). The US National Institute of Standards and Technology (NIST) Secure Software Development Framework, SP 800-218, lists reviewing human-readable code for vulnerabilities (practice PW.7) and testing executable code (practice PW.8) as two separate practices.
Coding
SAST in the IDE and on pull requests, plus SCA for dependencies
Every change
CI and staging
DAST against staging, IAST agent during the automated regression run
Nightly or per release candidate
Pre-release
Manual pen test scoped to new or changed features, especially login, payments, and user roles
Before each major release
Production
External pen test of the live app, plus lightweight DAST scans
At least yearly and after significant change
Block merges only on high-severity SAST findings, or developers learn to ignore the tool, and retest after every pen test, since an unverified fix is still an open finding.
On cadence, most teams start with an annual penetration test plus a retest after fixes. For applications that store, process, or transmit card data, PCI DSS requires penetration testing at least once every 12 months and after any significant change. Products in fintech, healthtech, or anything holding identity documents usually test more often. Our guide to penetration testing frequency covers how to set that cadence for your risk profile.
If you are starting from nothing, this order gets the most coverage for the least spend:
- Turn on SAST and dependency scanning in the repository.
- Add a DAST scan against your staging environment.
- Book a scoped penetration test before your next significant release or security review.
- Add IAST once you have an automated regression suite worth instrumenting.
If you need to make the budget case for that third step internally, here is why penetration testing is important for a product at your stage.
When a Lighter Setup Is Enough
Not every app needs all four layers. A marketing site with no login, no stored customer data, and a single contact form needs a DAST scan, a hardened server configuration, and regular dependency updates, and a full penetration test is poor value there. IAST is worth postponing until you have solid automated test coverage, because an agent watching three smoke tests analyzes very little. A penetration test on an app nobody has scanned yet spends expensive hours on findings a free tool would have reported.
The full combination earns its cost on any app with multiple user roles, payments, personal or regulated data, or enterprise customers who send security questionnaires.

How QAwerk Runs Web App Security Testing
At QAwerk, security testing sits inside the same team that does functional and regression testing. The QA engineers who build the regression suite know which flows matter, so DAST and IAST runs cover the paths real users take, and penetration testers start with the roles and business rules already mapped. A validation lead reproduces every finding and documents it with steps and evidence, so developers can pick it up in the next sprint.
We join at whatever stage the product is in, from a pre-launch app needing its first pen test to a live product facing its first enterprise security review. Engagements cover SAST code review and black, grey, or white box penetration testing, priced on Time and Material estimates with a realistic and a pessimistic range for each task. QAwerk has run penetration tests for fintech and identity-verification products, where authorization and session handling get the closest scrutiny.
Combine Static, Dynamic, and Manual Testing
No single testing approach catches everything. SAST keeps flawed code out early, DAST and IAST show what happens at runtime, and manual penetration testing finds the access and logic flaws automation misses. A real web app security program runs each of them at its own point in the SDLC. If you want that planned and run by one team, talk to us about your web app security through our web application testing services.
FAQ
What is the difference between SAST and DAST?
SAST analyzes source code without running it and points to the exact line of a flaw, so it runs early, on every commit. DAST tests the running application from the outside and finds configuration and runtime issues, so it needs a deployed build. They catch different problems, and most teams use both.
Is IAST a replacement for DAST?
IAST is more precise, but it only sees code paths your tests execute and needs an agent that supports your stack. DAST still checks the deployed web server, TLS settings, and headers, so the two work best together.
Can automated scanners replace a penetration test?
No. Scanners are good at known patterns such as injection and misconfiguration. They cannot judge whether a user should be allowed to see a record or skip a workflow step, which is where broken access control and business-logic flaws live. Finding those takes a human tester.
How often should a web application be security tested?
Run SAST and dependency scans on every change, DAST at least once per release, and a manual penetration test at least once a year and after significant changes. Apps that handle payments, health data, or identity documents usually need penetration tests more often.
What is the OWASP testing methodology?
It is the approach set out in the OWASP Web Security Testing Guide, which groups web app security tests into 12 categories, from information gathering and authentication testing to session management, input validation, and business logic. Testers cite its test IDs in their reports.
See a sample of our security code review of a US-based e-commerce platform